# Recent update to Debian install script
**URL:** https://discourse.nodered.org/t/recent-update-to-debian-install-script/95565
**Category:** General
**Created:** [22 February 2025 04:10 UTC](https://discourse.nodered.org/t/recent-update-to-debian-install-script/95565 "2025-02-22T04:10:51Z")
**Posts on this page:** 8
**Page:** 1
### Author:  [@jbudd](https://discourse.nodered.org/u/jbudd)
#### Post date: [22 February 2025 04:10 UTC](https://discourse.nodered.org/t/recent-update-to-debian-install-script/95565/1 "2025-02-22T04:10:51Z")
### Background
The additional security recommendations at the end of the installation script now look like this

The script now automatically runs `node-red admin init` and then **sets ownership of settings.js to root:root (0:0)**
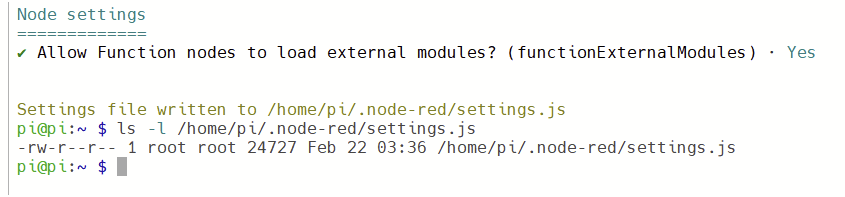
### Problem
#### 1
If you follow the advice and remove the 010\_pi-nopasswd file and subsequently run `node-red admin init` (eg to change the username/password or enable projects), it runs through all of the questions before finally failing with
```auto
Error: EACCES: permission denied, open '/home/pi/.node-red/settings.js'
```
(because the user no longer has write permission for settings.js)
#### 2
If you attempt to get around this by running `sudo node-red admin init` the first prompt is

If you fail to notice the significance of this and press on through the script, finally you see
```auto
Settings file written to /root/.node-red/settings.js
```
Start Node-red and the settings file just created is of course not used.

* * *
It is possible to envisage a test for sudo in `node-red admin` to avoid #2 but this whole situation arises because of the _demonstrably useless_ `chown 0:0 settings.js`
---
### Author:  [@dceejay](https://discourse.nodered.org/u/dceejay)
#### Post date: [22 February 2025 09:04 UTC](https://discourse.nodered.org/t/recent-update-to-debian-install-script/95565/2 "2025-02-22T09:04:57Z")
We can certainly undo that change - but it's "demonstrably useless" in the same way that people wearing seat belts still die in car accidents, so we should remove them.
---
### Author:  [@TotallyInformation](https://discourse.nodered.org/u/TotallyInformation)
#### Post date: [22 February 2025 11:39 UTC](https://discourse.nodered.org/t/recent-update-to-debian-install-script/95565/3 "2025-02-22T11:39:05Z")
> [@jbudd](#):
>
> demonstrably useless
Can you please explain this statement for clarity.
---
### Author:  [@jbudd](https://discourse.nodered.org/u/jbudd)
#### Post date: [22 February 2025 12:07 UTC](https://discourse.nodered.org/t/recent-update-to-debian-install-script/95565/4 "2025-02-22T12:07:22Z")
Node-red is a powerful multi-purpose programming language.
Password protecting it is a viable, minimal, security change because once someone can create and deploy flows they can do whatever they want.
Removing passwordless sudo access is also a sensible precaution because it limits Node-red's ability to change system files.
It is a good idea to protect settings.js from malicious changes.
A malicious Node-red user can change or delete any security precautions in settings.js. They can change the user account and password, decrypt credentials, allow function nodes to load external modules, remove any proxy or middleware options specified there.
And after `chmod 0:0 settings.js` they can make it writable and **still do all of the above**.
`chmod 0:0 settings.js` is "demonstrably useless" because I have shown you a simple flow that, without using sudo, can reverse it.
I have also shown how you can prevent this, but it requires changes to the core code.
Someone, perfectly reasonably, chose not to include this precaution in NR v4.
> [@On another topic](https://discourse.nodered.org/t/82487/2):
>
> [Oct 2023]
> Secure by default for the next major version [v4] has been discussed between the core Devs. Nothing is set in stone or decided yet, just letting you know it has been discussed. Watch this space.
In your analogy, `chmod 0:0 settings.js` is the equivalent of fitting a car with tissue paper seatbelts.
> [@TotallyInformation](#):
>
> Can you please explain this statement for clarity.
I will send you the details by PM.
---
### Author:  [@jbudd](https://discourse.nodered.org/u/jbudd)
#### Post date: [22 February 2025 12:16 UTC](https://discourse.nodered.org/t/recent-update-to-debian-install-script/95565/5 "2025-02-22T12:16:55Z")
> [@dceejay](#):
>
> We can certainly undo that change
The point of this thread was to point out that the advice given at the end of the installation does not work.
I really don't want to revisit questions of Node-red security.
---
### Author:  [@jbudd](https://discourse.nodered.org/u/jbudd)
#### Post date: [5 March 2025 00:40 UTC](https://discourse.nodered.org/t/recent-update-to-debian-install-script/95565/6 "2025-03-05T00:40:31Z")
Today I stumbled upon the Linux command chattr (and lsattr, both available on Debian at least) which among other options, can be used to make a file immutable even by the superuser.
From `man chattr` :

At first sight, this might be appropriate advice at the end of the install script:
```auto
echo " - After running Node-RED for the first time, prevent changes to the settings file"
echo " "
echo " sudo chattr +i ~/.node-red/settings.js"
echo " "
```
---
### Author:  [@dceejay](https://discourse.nodered.org/u/dceejay)
#### Post date: [5 March 2025 00:46 UTC](https://discourse.nodered.org/t/recent-update-to-debian-install-script/95565/7 "2025-03-05T00:46:37Z")
Nice find. Certainly worth testing to see if is less “ demonstrably useless”
---
### Author:  [@system](https://discourse.nodered.org/u/system)
#### Post date: [3 June 2025 00:47 UTC](https://discourse.nodered.org/t/recent-update-to-debian-install-script/95565/8 "2025-06-03T00:47:13Z")
This topic was automatically closed 90 days after the last reply. New replies are no longer allowed.